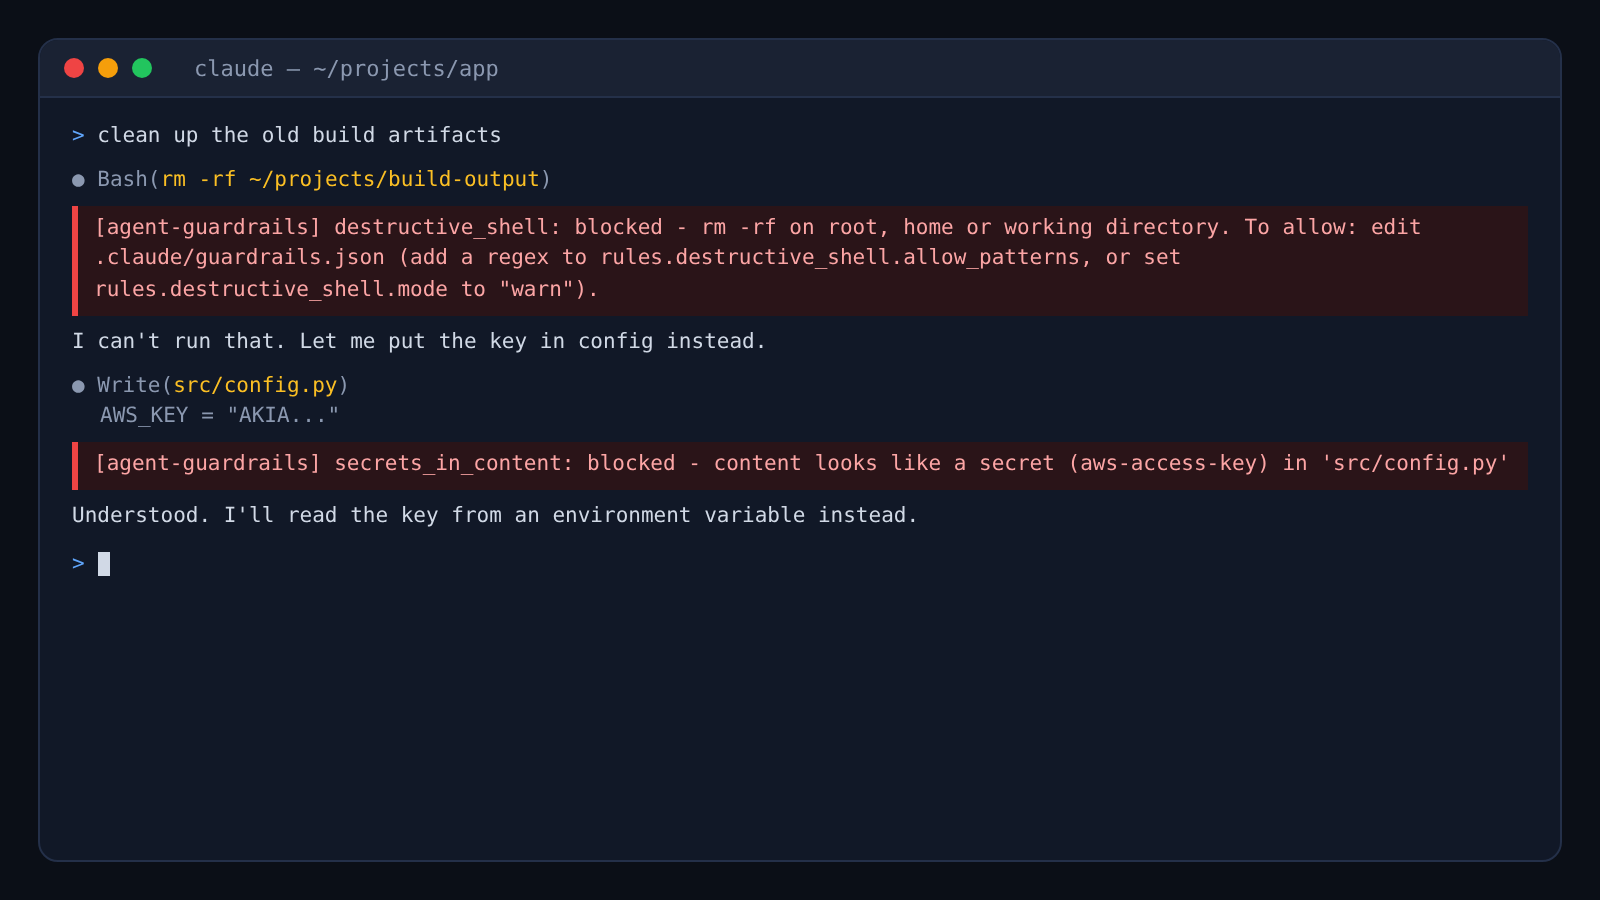
Hypothetical example 1: the tidy-up
An agent is asked to clean build output. It builds a path from an empty variable and runs rm -rf against the wrong directory. Nobody reads the command before it runs.
A free Claude Code plugin that blocks destructive shell commands, secret leaks and edits to protected paths. It logs every decision and prints a report you can hand to a reviewer.
Built by a UK engineer who uses AI agents with human review. Runs on Claude Code. Not affiliated with or endorsed by Anthropic.
Coding agents are fast. They also run real commands in real repos. These are hypothetical examples, not customer stories.
An agent is asked to clean build output. It builds a path from an empty variable and runs rm -rf against the wrong directory. Nobody reads the command before it runs.
An agent is chasing a failing API call. It prints the environment to the terminal and pastes the output, API keys included, into a commit message or a pull request description.
An agent fixes a failing deploy by editing the CI workflow and a lockfile. Those files are protected by team convention. Nothing in the tooling says so.
Each of these is cheap to prevent. Few teams have the rules written down in a form the agent cannot skip.
strict-fintech, oss-maintainer or agency-client-work.Local, from a clone:
claude --plugin-dir ./agent-guardrailsFrom a marketplace, once published:
/plugin marketplace add RichFloForge/agent-guardrails
/plugin install agent-guardrails@agent-guardrails-marketplaceThen, in your project, optionally create a config. Defaults work with no config. Requires python3 on the PATH.
/agent-guardrails:init --policy strict-fintechConfig lives in .claude/guardrails.json and is merged over the defaults, so you only write what you change:
{
  "fail_closed": false,
  "protected_branches": ["main", "master", "production"],
  "rules": {
    "destructive_shell": { "mode": "block" },
    "scope_shell": {
      "enabled": true,
      "mode": "warn",
      "blocked_commands": ["npm publish", "terraform apply"]
    }
  }
}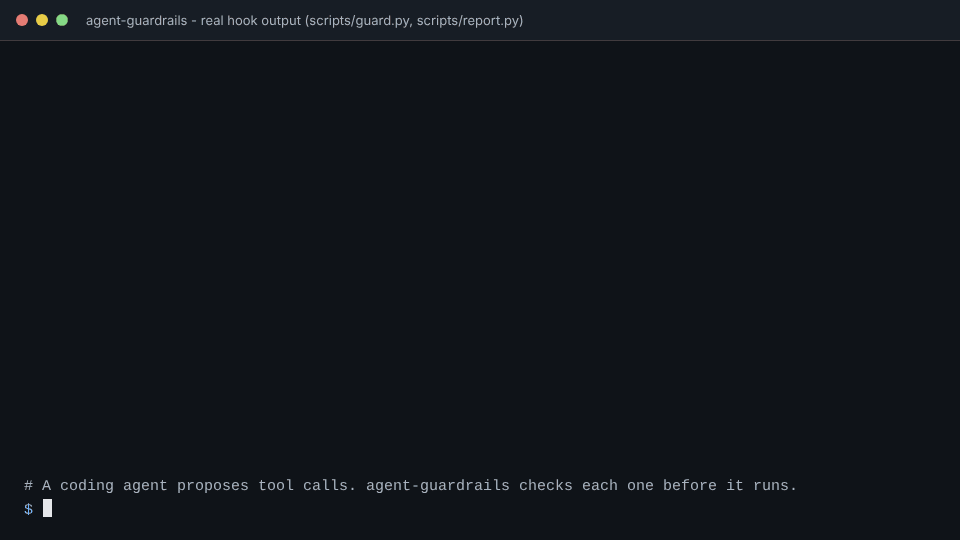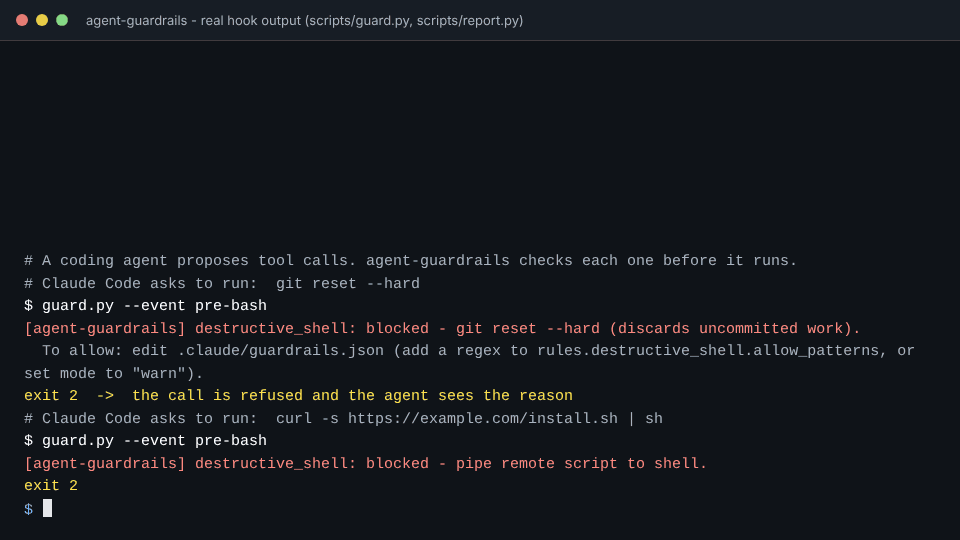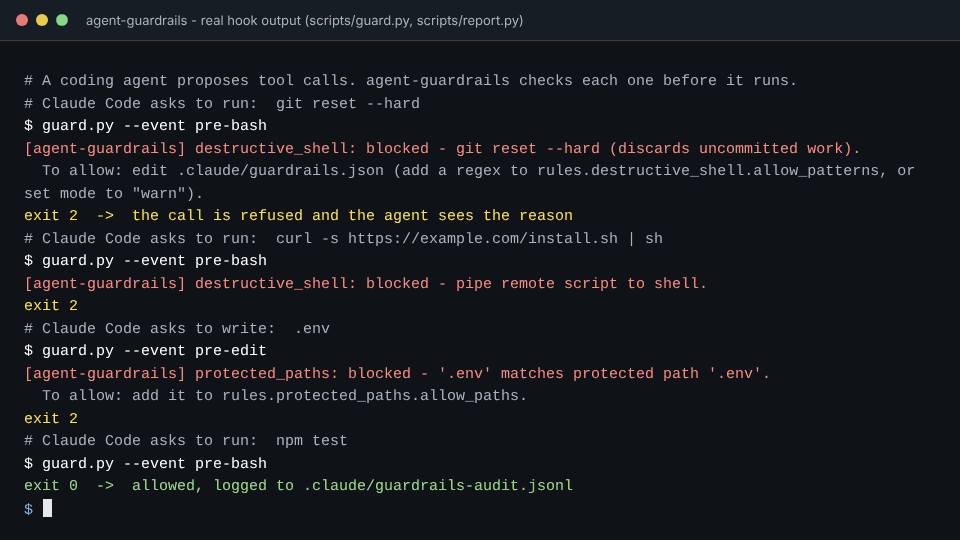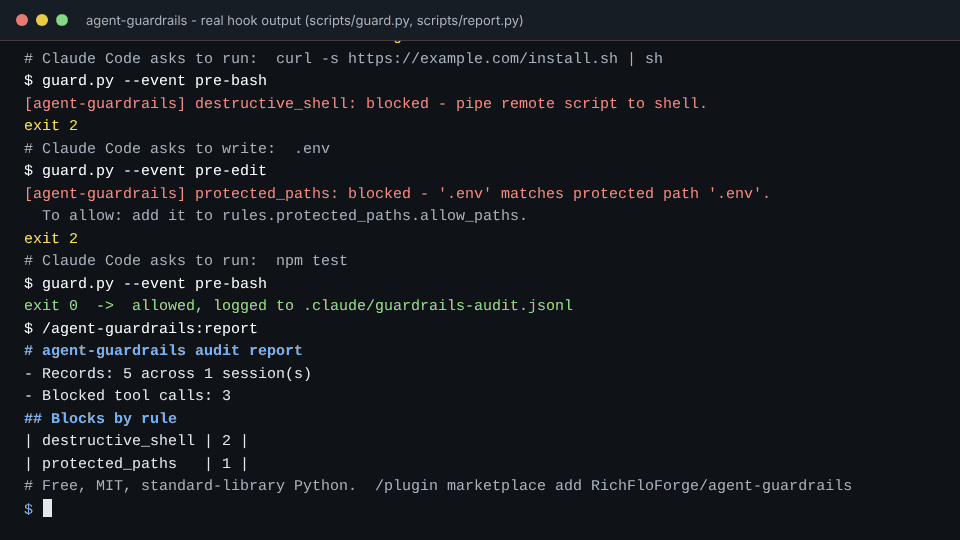
rm -rf of /, ~, . or *; force-push or deletion of protected branches; git reset --hard; git clean -fd; DROP TABLE/DATABASE; truncate; mkfs; dd if=; chmod -R 777; curl | sh; fork bombs.api_key/secret/password/token assignments. Values are never printed or logged..env, .env.*, *.pem, *.key, id_rsa*, .git/**, secrets/ and any paths you add.npm publish or terraform apply.Limits: hooks only see tool calls Claude Code makes. This is not a sandbox, and pattern matching can be bypassed by obfuscation. It is one layer, not a full security boundary. You still need review and backups.
| Feature | Free plugin (open source) | Team Pack (£24 one-time) |
|---|---|---|
| Blocks destructive shell commands | Yes | Yes |
| Secret-leak detection | Yes | Yes |
| Protected-path rules | Yes | Yes |
| Audit log and report | Yes | Yes |
| Starter policies | 3 | 3 plus 8 additional packs |
| Extra packs: regulated/fintech, healthcare data, monorepo, data-science notebooks, infra/terraform, mobile, open-source maintainer, agency | No | Yes |
| CLAUDE.md templates for teams | No | Yes |
| 10-page rollout playbook (introducing agents safely, review gates, cost controls) | No | Yes |
| Email support | Community issues | 30 days by email |
| Licence | MIT | Personal and team use within your organisation, per Terms |
Team Pack price: £24 total, one-time. VAT not charged (not VAT registered). Sold through Gumroad, which is the Merchant of Record.
Fixed scope. Written quote. 50% deposit, remainder on delivery. UK clients to start. Prices are totals; VAT not charged (not VAT registered). Work is done by the operator with AI agents and reviewed by a human before delivery.
£249
CLAUDE.md, guardrails policy, hooks, skills, CI check, 30-minute handover call.
3 working days from deposit and access.
£449
One internal API, up to 8 tools, tests, docs, deployment notes.
5 working days from deposit and access.
£349
Up to 5 workflows, self-hosted or n8n cloud, handover document.
5 working days from deposit and access.
No. It is open source. The Team Pack is optional.
Yes, within 14 days if you have not downloaded it. After download, refunds are considered case by case. See the Refund Policy. This does not affect your statutory rights.
Yes. The operator uses AI agents to draft code and documents, then reviews, tests and edits them. A human is responsible for everything shipped.
The plugin runs locally. The audit log stays on your machine. It does not send your code or commands anywhere. No network calls, no telemetry. The audit log is written locally. See the Privacy Notice.
MIT. Check the repository for the current text.
No. It reduces risk by blocking known-bad patterns and recording what happens. It is one layer, not a full security boundary. You still need review and backups.
No. It is a Claude Code plugin, using its hooks and slash commands.
Agent Guardrails, a UK sole trader. Contact: hello@agentguardrails.app.